invests in resilient systems with protection

Our thesis

We back computing infrastructure, software products, and protocols that protect private information and owned value through cryptography a user can verify.

Our investment thesis

Confidential Work. Verifiable Ownership. Scalable Protection.

The thesis moves from systems that protect confidential work, to protocols that support verifiable ownership, to products that carry those protections into use.

Confidential Work

AI systems process sensitive information and act through connected tools. Much of that work still depends on trust in the operator. We invest in systems that can protect confidential work when operator trust alone is not enough.

Technical context

Confidential computing can protect data while it is processed. Attestation provides evidence about the environment running a model. Least-privilege controls limit an agent's access and actions. Evidence for one does not establish the others. We assess whether the controls hold in production, what they cost, and whether their use supports company revenue or demand for an underlying asset.

Verifiable Ownership

A public ledger can make a transfer verifiable while exposing holdings. Custody can simplify access while placing control of keys with an intermediary. We invest in protocols and wallets designed to let people and institutions hold and move value without surrendering key control or making every holding public.

Technical context

Zero-knowledge proofs can establish transaction validity without publishing protected details. Self-custody keeps spending keys with the owner, while open networks can allow participation without a central gatekeeper. We review code and on-chain activity to assess how these protections compose in deployed systems.

Scalable Protection

Systems for confidential processing, controlled AI workflows, and protected value movement become useful when they work in everyday products. We look for products, protocols, and networks that can make those protections practical as use grows.

Technical context

In regulated settings, products may need to control where data is processed, who can access it, and how long records are kept, while maintaining an account of system activity. We assess whether these controls work together in use, and how companies or assets capture value as adoption grows.

How we research

Root Storms (Opens in a new tab) supports our opportunity diligence through technical, UX, and security research. Its work helps us examine code, architecture, user experience, and security assumptions.

What active networks are telling us

Shielded Value

Zcash held in shielded pools

—ZEC

90 days in ZEC. Select a point to inspect.

Explore the protocol

NEAR

Validator concentration and model attestation support

—%

Largest validators by stake. Select a bar to inspect.

Explore the protocol

Pearl

Non-coinbase transactions

—transactions

30 complete UTC days. Select a day to inspect.

Explore the protocol

Research across markets

Research across these markets puts technical developments in the context of local demand, infrastructure, and regulatory requirements.

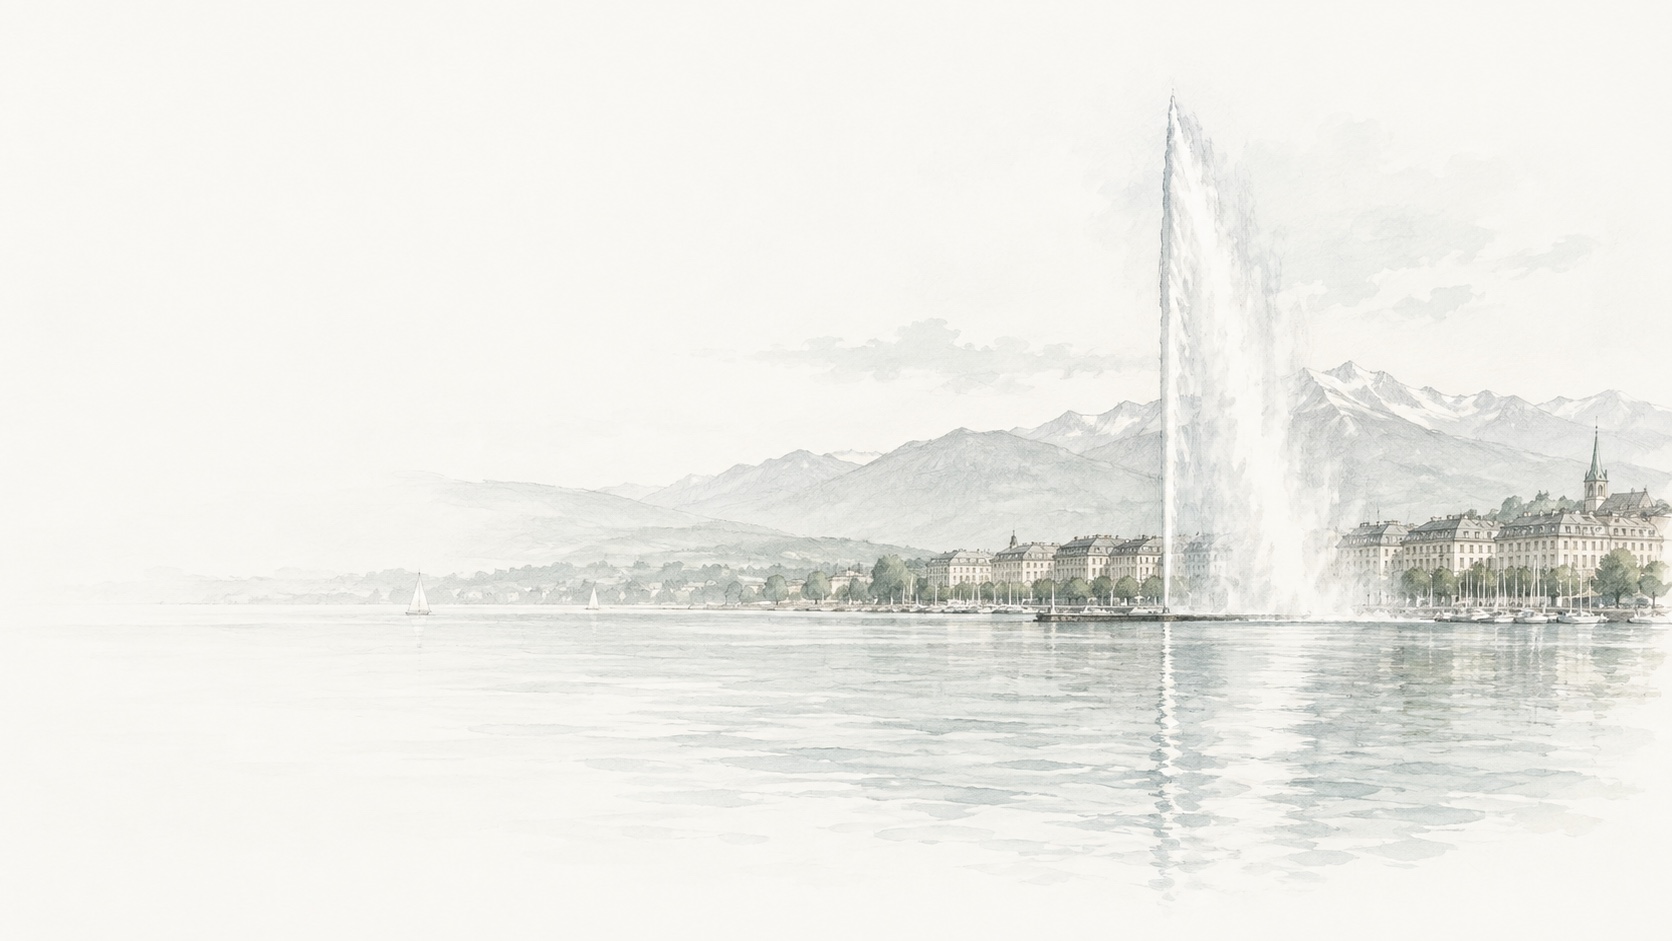
Architectural watercolor illustration of Geneva’s Jet d’Eau and Lake Geneva

Geneva

. Our research in Geneva follows privacy technology and its adoption across communication services, financial infrastructure, and confidential analysis.

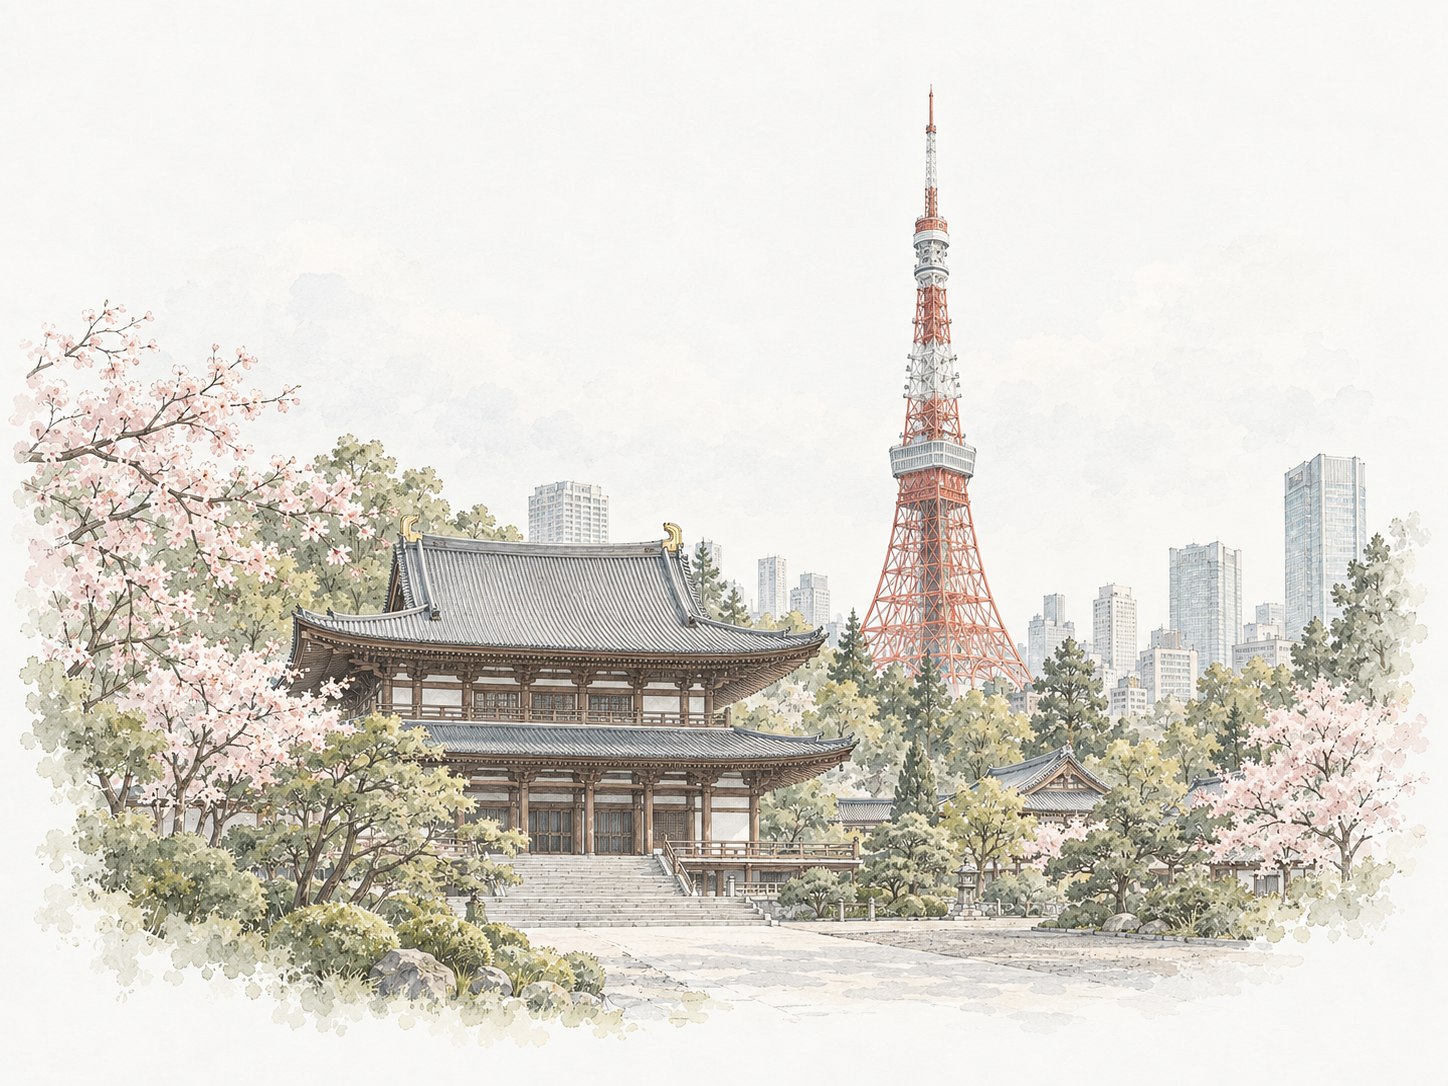
Architectural watercolor illustration of Tokyo Tower and a traditional temple in Tokyo

Tokyo

. Our Tokyo research follows privacy technology in Japanese business, from JAL and DOCOMO’s travel analysis without exchanging source records to NTT’s confidential computing service.

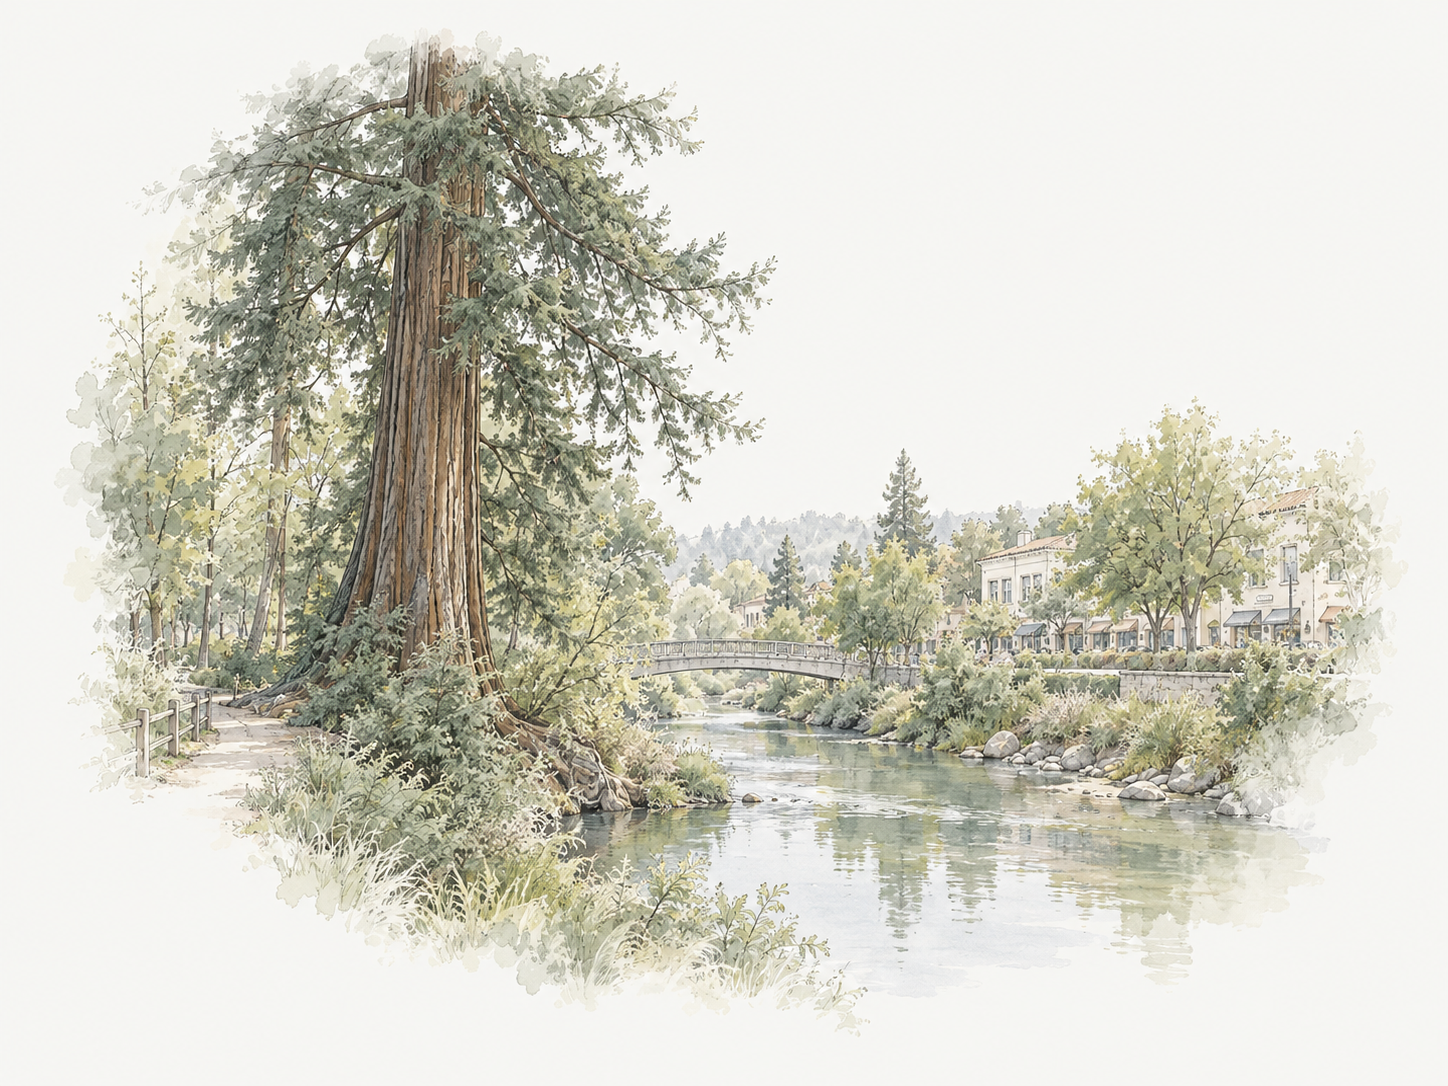
Watercolor illustration of a coast redwood and creek in Palo Alto

Palo Alto

. In Palo Alto and the wider Bay Area, our research follows the economics of confidential computing, the product choices that shape adoption, and the investment behind new software and infrastructure.

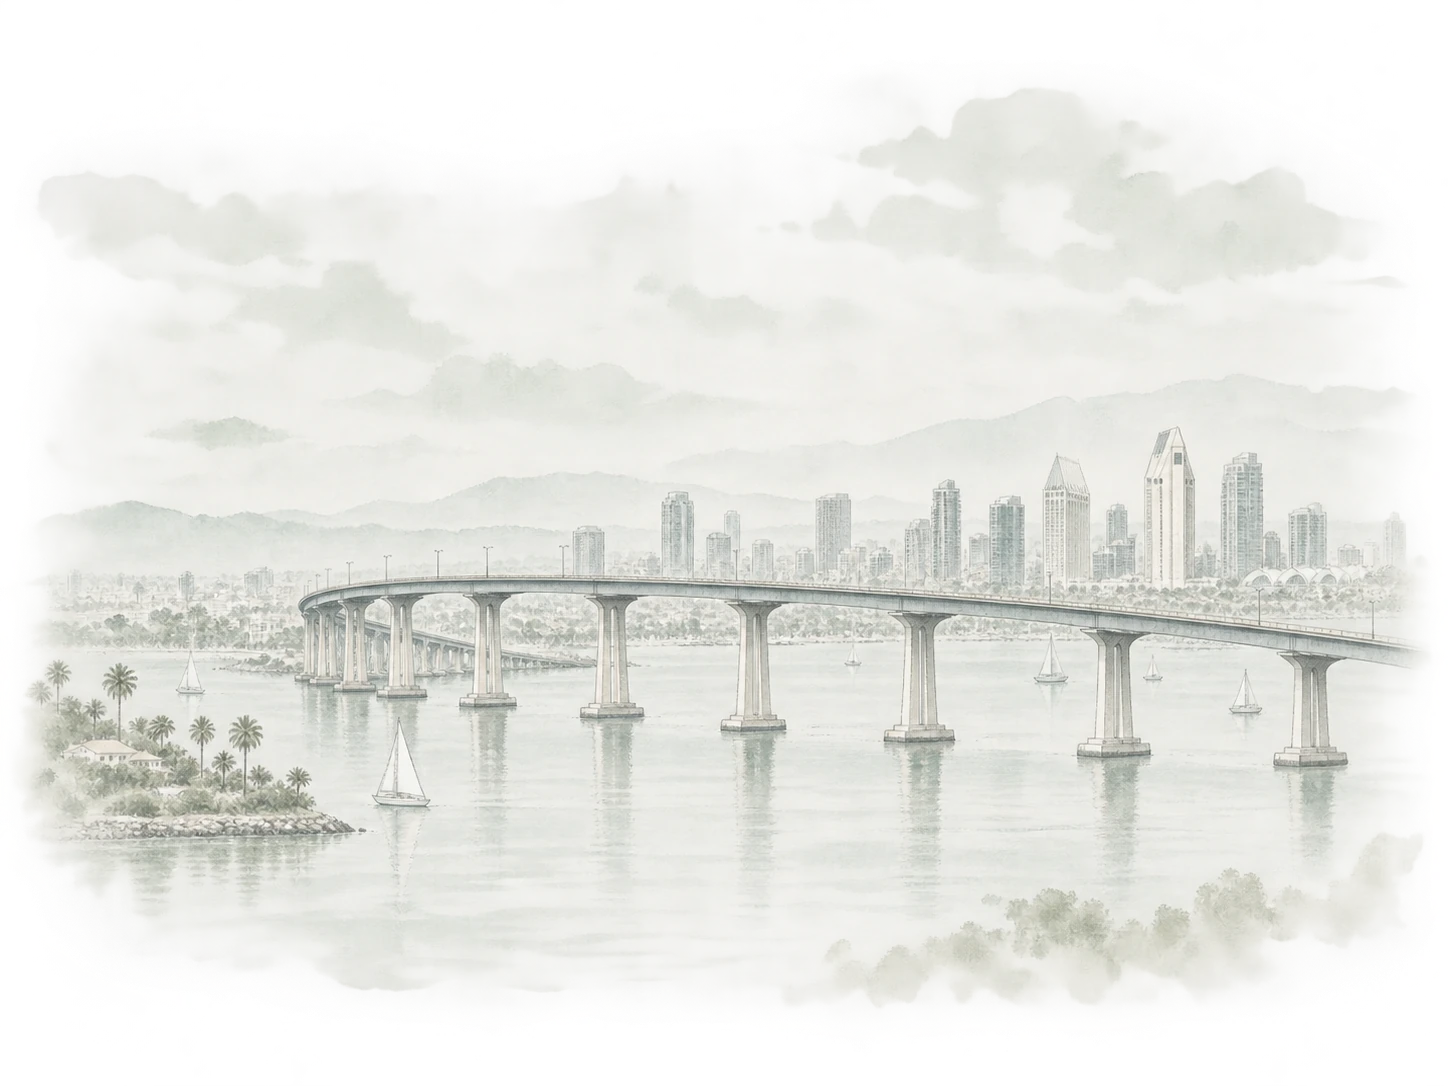
Architectural watercolor illustration of Coronado Bridge and the San Diego skyline

San Diego

. Our research in San Diego follows encrypted clinical analysis and the integrity of models built across institutions, alongside how AI fits into patient care.

Root Storms updates

    Skip to the investment thesis
    AIGIS

    Investment thesis

    AIGIS invests in companies and networks that protect private information and asset ownership. Our conviction is that as AI takes on more sensitive work and software controls more value, effective protection will become a stronger reason to choose one product over another.

    The opportunity spans infrastructure that makes protection possible and products that make it useful. We look for technology that addresses a real need, a practical path to adoption, and a way for that adoption to produce investment returns. We view privacy as a core requirement of the infrastructure people rely on. Capabilities, cost, and ease of use shape how widely that protection is adopted.

    Verifiable protection

    Users should be able to check a system’s protection, not just read its description. We look for evidence tied to the deployed system: who can access data, who can move assets, what environment ran the work, and whether a claimed result is valid. Its limits and the trust it still requires must be clear.

    Different products serve different needs. A payment network may prioritize keeping transaction details private. A consumer application may improve privacy while preserving familiar features and user choice. An organization may need controls over where data is processed and who can access it.

    We assess protection against the risks a product addresses and the people it serves. Cost, performance, convenience, and recovery options all affect adoption. There is room for different approaches, provided their protection claims can be checked and their limits are clear.

    Adoption and investment value

    Protection can create investment value by helping products win and retain users or enabling work that would otherwise be too risky. We assess who pays, why they stay, and what competitors can reproduce. Technical quality needs distribution and sustainable business or network economics.

    For equity, we assess revenue, costs, competitive advantage, and valuation. For network assets, we examine what the asset does, how usage creates demand for it, and how supply, incentives, and governance affect holders. Growing network use is only part of the investment case. Price, liquidity, and position risks must support the returns we seek.

    Root Storms supports our opportunity diligence through technical, UX, and security research. That research helps us examine code, user experience, security assumptions, and deployment constraints alongside evidence of adoption and business or network economics.

    How we test the thesis

    We follow actual use: does protection influence product choice, do users stay, and does their activity support the economics we expect? Demand for privacy starts the research. Adoption, economics, price, and risk guide the investment decision.

    Existing platforms may meet these needs, protections may become standard features, or users may find the tradeoffs too costly. Security failures, weak distribution, or poor investment terms can undermine an otherwise useful product. We reassess a position when the evidence no longer supports its technical, commercial, or return assumptions.